Your top two priorities for 2026 are actually one problem.
State CIOs just ranked AI first and cybersecurity second. For the first time in 12 years, AI outranks cyber in the NASCIO Top Ten. Most agencies are staffing them as two separate programs.
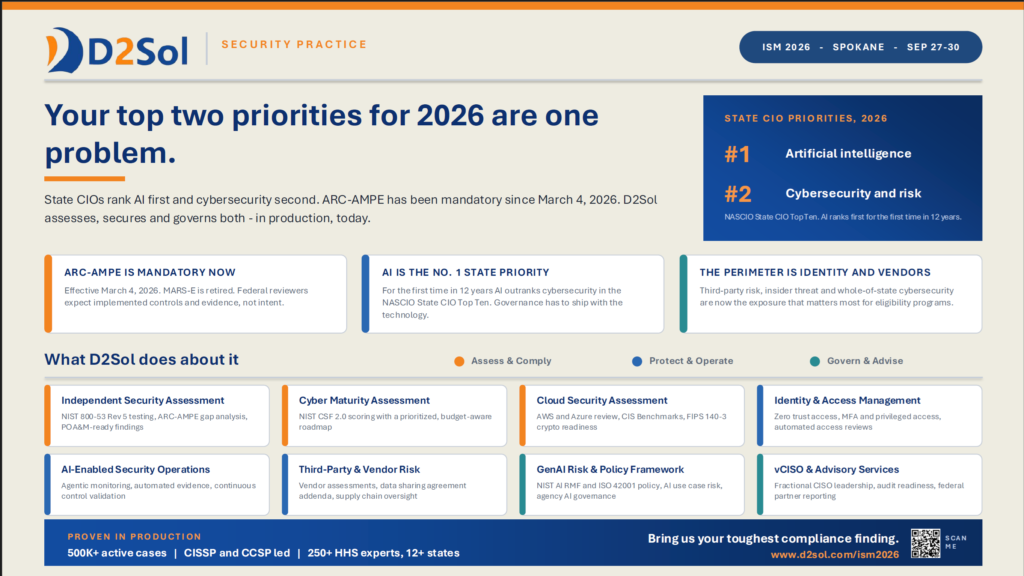
They are not separate. An AI use case in eligibility touches the same PII, the same FTI, and the same federal reviewers as everything else in your environment. Governance that ships after the technology is governance that fails an audit.
Here is how we work the two together:
- Assess and comply: NIST 800-53 Rev 5 control testing, ARC-AMPE gap analysis, POA&M-ready findings
- Protect and operate: zero trust access, agentic monitoring, continuous compliance evidence
- Govern and advise: NIST AI RMF and ISO 42001 aligned policy, AI use case risk assessment, vCISO leadership
We do this in production today, for an integrated eligibility platform serving 500K+ active cases.
Talk security with us at ISM 2026, Spokane Convention Center, September 27-30.